Ransomware-Proof Enterprise Cloud Backup & Business Continuity Vaults
We engineer automated, immutable off-site cloud backup frameworks to secure corporate databases, financial ledgers, and server images. Protect your operations from drive failures, accidental deletions, and ransomware encryption loops with verified daily restoration passes across Kolkata, Ahmedabad, and PAN-India business hubs.
The Vulnerabilities of Traditional Data Backup Methods
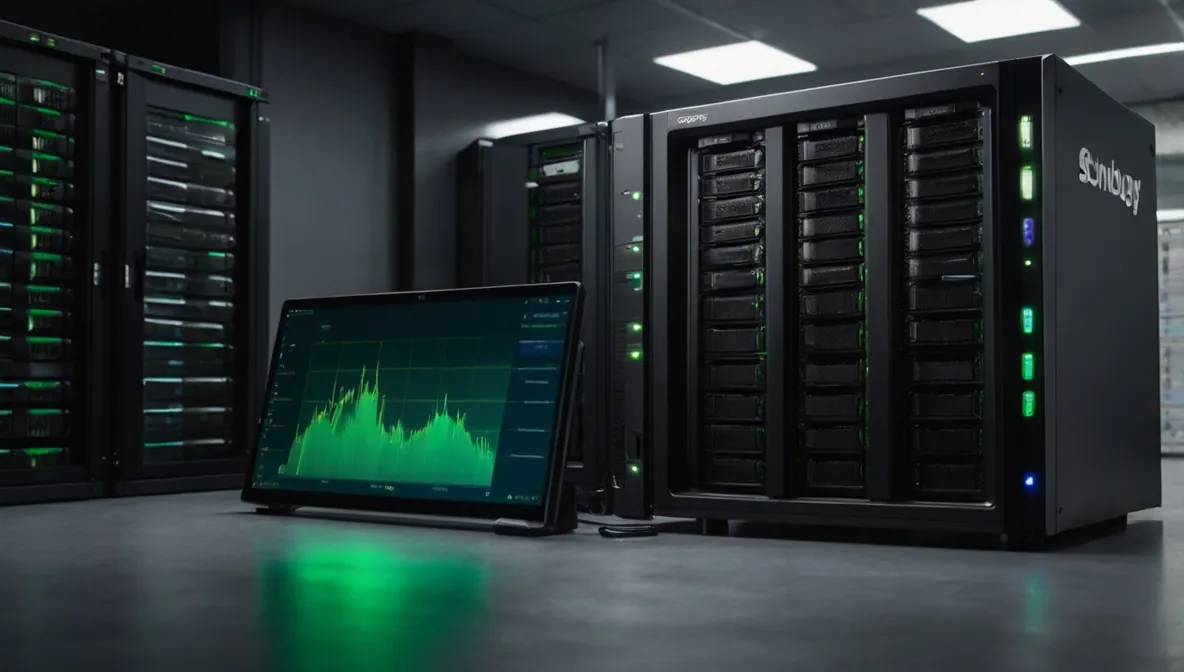 Figure 1: High-availability data backup matrix combining local NAS pre-staging with encrypted cloud replication.
Many businesses still rely on loose USB hard drives sitting on an accountant's desk or basic consumer file-sync services like OneDrive or Google Drive for corporate backups. An external drive physically connected to the network is fully vulnerable: if ransomware enters the network, it targets and encrypts connected local drives first.
Similarly, standard cloud synchronization tools mirror file changes rather than maintaining independent recovery states. If a file is accidentally deleted, overwritten, or corrupted by ransomware, that change synchronizes across cloud accounts immediately, leaving you with a synced copy of unusable data. True resilience requires isolated, multi-version snapshots stored completely outside the active network environment.
The Financial Reality of Corporate Data Loss
Company databases and project files form the backbone of everyday business operations. Losing financial ledgers, ERP records, or transactional histories halts daily work immediately. The real financial impact lies in sustained operational downtime: staff cannot invoice, dispatch lines freeze, and overhead mounts for every hour systems remain inaccessible.
Deploying immutable cloud backup vaults eliminates this exposure. Servers, virtual machines, and endpoint computers upload encrypted, incremental snapshots automatically to an air-gapped repository. If local hardware fails or malware encrypts active systems, you wipe the machine and roll back to a clean snapshot taken minutes before the incident, bypassing extortion demands entirely.
Real-Life Scenario: Restoring an Empty Shortcut Trap
Data protection strategies require verified mock restoration drills rather than reliance on automated success emails. We once assisted an engineering firm that believed their backups were running reliably because their software dashboard displayed a green "Success" status daily. When an internal server drive failed, they discovered a severe configuration error.
A software update had altered directory paths, causing the backup script to copy an empty 1KB shortcut rather than the actual live ERP database. The software logged the shortcut transfer as successful, leaving the live data unbacked for months. Our integration lab had to execute a complex manual recovery to salvage their records. That experience is why we run routine restoration passes to confirm that backup archives can be fully restored when an emergency occurs.
| Data Vector Profile | The Standard SME Vulnerability | Our Immutable Backup Vault Standard | Operational Continuity Impact |
|---|---|---|---|
| Storage Architecture | Single local drive copies vulnerable to fire, theft, or local water damage. | Strict 3-2-1 rule execution with localized NAS pre-staging and off-site cloud mirrors. | Guarantees data survival even if your physical building is completely inaccessible. |
| Ransomware Defense | Connected network shares that can be modified or deleted by local malware. | Write-Once-Read-Many (WORM) immutability flags locked at the root storage block. | Malicious software strings cannot encrypt or wipe your historical archive states. |
| Recovery Time (RTO) | Days spent reinstalling operating systems and patching data fields manually. | Bare-Metal recovery allowing full system state restoration to alternate hardware fast. | Reduces server restoration windows from days down to under an hour. |
| Data Verification | Assuming backup scripts are functional based on unverified automated emails. | Automated block-level verification passes and routine mock restoration testing drills. | Ensures zero file corruption when you need to pull down data during a crisis. |
Common Backup Blunders: The Illusion of Security
A frequent error is failing to define a clear Recovery Point Objective (RPO). Running full, uncompressed backups across active internet lines during the business day chokes office bandwidth, causing application timeouts and lagging communications. Backup routines must be scheduled with block-level deduplication to run silently during off-peak hours.
Another common mistake is assuming that SaaS providers (like Microsoft 365 or Google Workspace) automatically keep point-in-time historical backups. They operate on a shared responsibility model, maintaining platform uptime while leaving file deletion and retention management to the client. Independent cloud-to-cloud archiving is required to prevent accidental or malicious file purges.
The Sequential Roadmap for High-Availability Data Protection
- Map out critical data paths: Identify where primary databases, accounting software paths, and configuration records reside across all systems.
- set up daily block-level deduplication: Transfer only changed data blocks rather than entire database files to conserve bandwidth and reduce storage costs.
- separate backup credentials: Store backup vault administration credentials outside your primary area directory to prevent compromised accounts from tampering with archives.
- Enforce WORM immutability: Apply Write-Once-Read-Many retention locks so historical snapshots cannot be deleted or altered by any user or application during the retention window.
- make sure network stability: keep certified copper and switch routing to make sure backups transfer cleanly, aligning with our SME IT Optimization blueprints.
Frequently Asked Questions (FAQs)
What is an "immutable" backup and how does it stop ransomware?
An immutable backup locks uploaded snapshots using Write-Once-Read-Many (WORM) storage protocols. Once data enters the vault, snapshots cannot be modified, overwritten, or deleted by any user or malware string until the retention period expires, ensuring historical states remain clean.
How long does it take to restore a full database after a crash?
Under our hybrid 3-2-1 model, file-level restorations complete in minutes directly from a local on-site NAS. In a complete server loss, bare-metal restore images allow spinning up the operating system, applications, and data onto alternate hardware or a cloud VM in under an hour.
Will running daily backups slow down our office internet connection?
No. Using block-level tracking and compression, our systems only upload minor text changes and modifications made since the previous run. Intensive synchronization routines are scheduled during off-peak night hours, leaving daytime bandwidth unaffected.
Our Hardened Cloud Resiliency Stack
- Hybrid 3-2-1 Architecture Setup: Provisioning and managing local NAS appliances (Synology, QNAP) paired with secure, remote cloud endpoint replication nodes.
- Immutable Vault Provisioning: Setting up ransomware-proof off-site data pools using Acronis Cyber Cloud platforms to promise file survival.
- M365 & Workspace Cloud-to-Cloud Backups: Independent, automated archival protection for corporate emails, SharePoint directories, and team collaboration files.
- Bare-Metal Server Image Backups: Creating full system state snapshots of Windows Server, VMware, and Hyper-V host layouts for rapid disaster recovery.
- Daily Verification Logs: Continuous monitoring of data block integrity and routine mock restoration exercises, supported by our Remote Managed IT support desk.